Autonoma
swipe to navigate
Overview
Autonomous, state-aware web security crawler that maps every page and interactive element of an app, tests each one for functional bugs and OWASP vulnerabilities, and reports findings through a live React control console.
The Challenge
Manual QA and pentest coverage rarely scales with how fast an application's pages and forms change. Autonoma maps a target app end-to-end (every page, every form, every button), then runs a coordinated set of agents against each element: a baseline pass to establish clean behavior, a chaos/abuse pass for functional bugs, an OWASP payload pass for security vulnerabilities, and an LLM-driven business-logic pass for the gaps rule-based testing misses.
The Solution
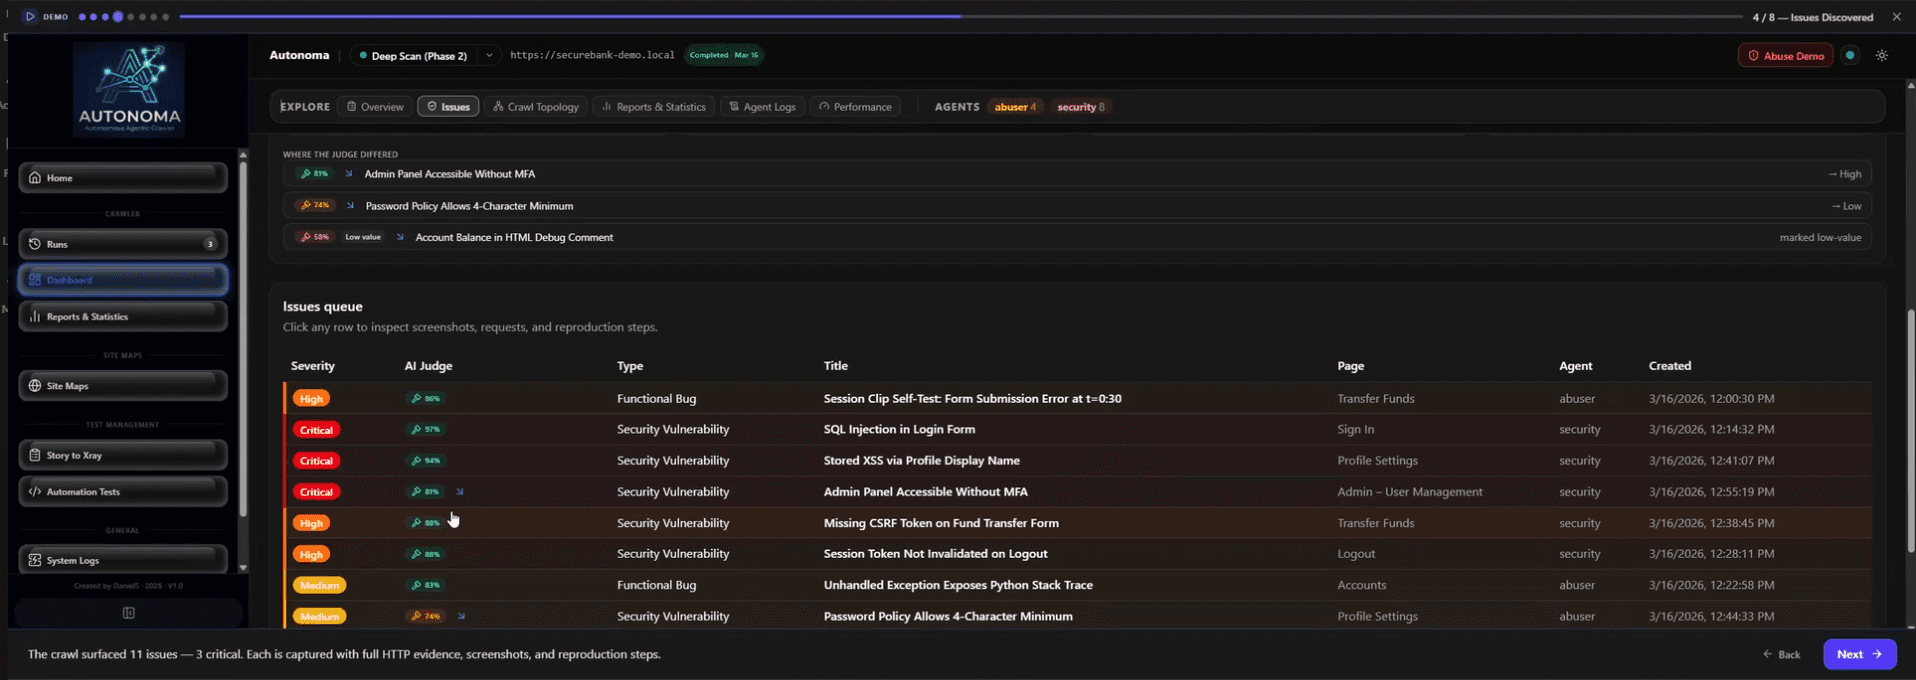
A React control console lets you start scans, watch progress live, and drill into every finding with reproduction steps and evidence.
Key Features
- ✓Autonomous crawl: DFS traversal maps every reachable page and groups interactive elements (forms, navigation, action buttons).
- ✓Mixed public/auth scan: public pages are crawled without cookies; once a login page is found, the crawler performs one authenticated login, then continues testing protected pages with that
- ✓Multi-agent testing: Baseline (clean behavior), Abuser (functional chaos: empty/overlong inputs, Unicode, double submits), Security (SQL injection variants, XSS), and Analyst (LLM-driven bu
- ✓Runs dashboard: every crawl is a "run" with its own issues, tasks, logs, and topology (graph, tree, and network views).
- ✓Issues viewer: full reproduction detail: HTTP evidence, console errors, screenshots, and a session video clip centered on the issue.
- ✓Live browser stream: watch each crawl worker's browser live via MJPEG.
- ✓Story to Xray Tests: generate Xray manual test cases from a Jira story using an LLM, review/edit, and push to Jira.
- ✓Automation Tests: generate Playwright TypeScript tests from a manual test case and the crawl's site map, run them in-browser, and auto-heal failing tests by reading Playwright's accessibili